IT & Cybersecurity
IT and cybersecurity consulting focused on restoring coverage, control, and provable trust.
WHY CORDATUS
Stay Covered, Stay Audit-Ready by Default
An overdue access review is rarely your only problem. Behind it, a former contractor may still hold a live token, a service account may have kept domain rights for two years, and no one on your team can say who approved either. Your patch cadence slips as backlogs grow. A third of your laptops may report to an EDR console that stopped receiving check-ins months ago, and your incident response runbook has never been tested. Then a SOC 2 auditor asks for evidence, or a client sends a ninety-question security assessment, and your team scrambles against the deadline to rebuild answers from logs that were never meant to provide them.
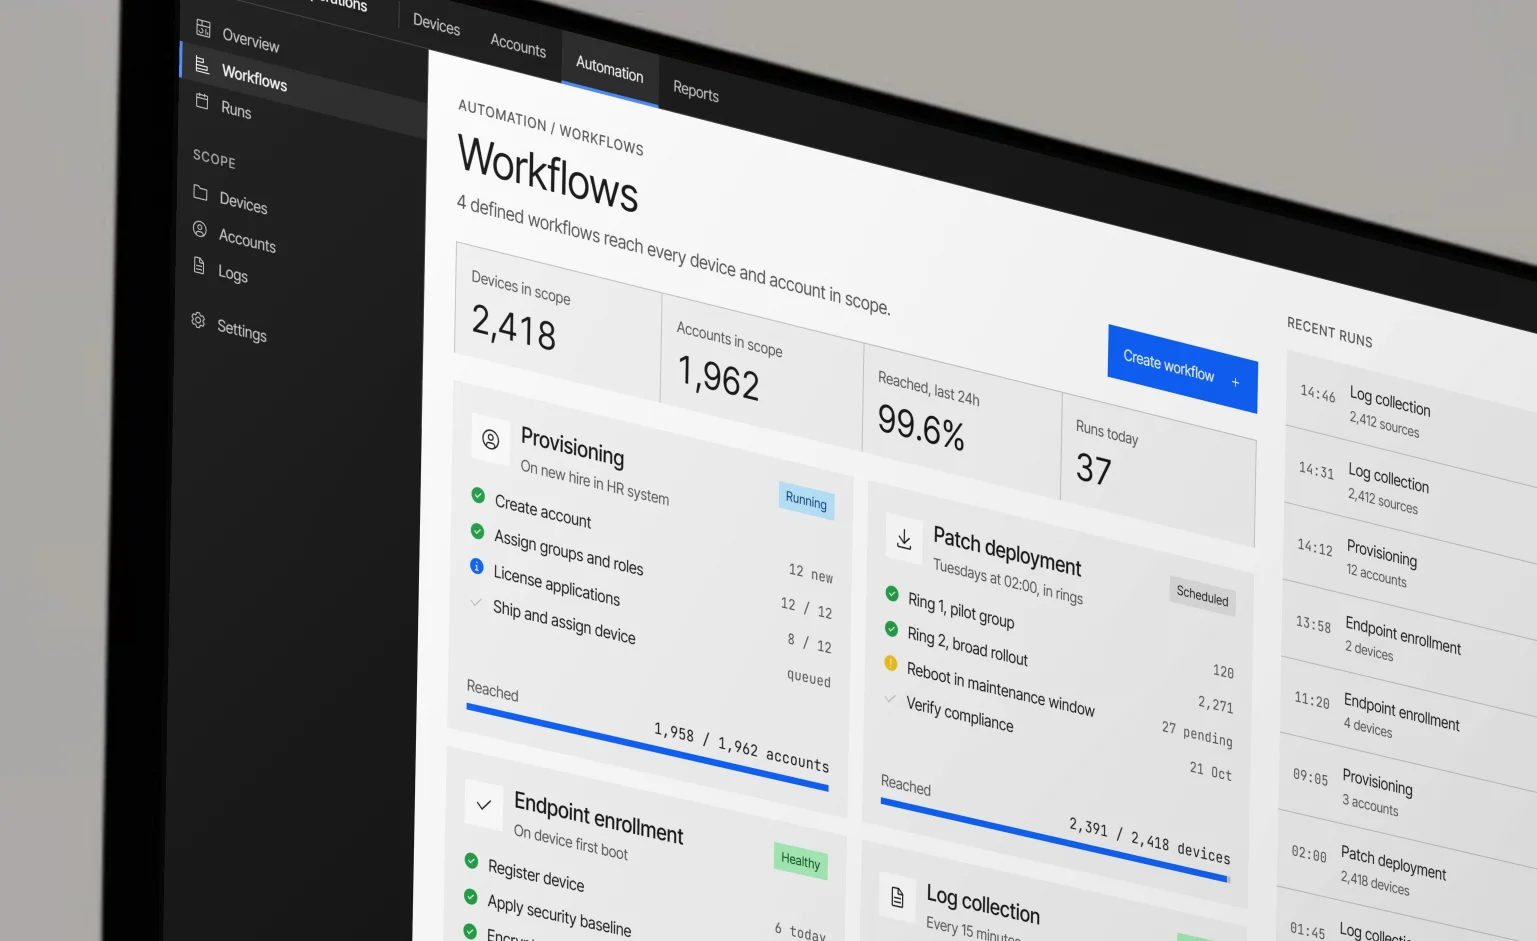
Put your IT and security function on an operating system that keeps every device and account covered and your record continuous. Endpoint administration, patching, and identity provisioning run on defined workflows, and automation handles the routine volume, so your IT director and security lead can focus on the risk decisions and exceptions they own. Access reviews and control checks run on a fixed cadence, and every action captures the evidence your framework will require before anyone asks for it. You stay covered day to day, and when an auditor or client asks for proof, it’s already there.
OUR EDGE
Automate the Routine and Keep Control of Risk

Automation With Coverage
Provisioning, patch deployment, endpoint enrollment, and log collection run on defined workflows that reach every device and account in scope. Coverage holds as the infrastructure grows and staff changes. Only actionable alerts reach your team, allowing security leads to direct their attention toward high-exposure risks.
Specialists Own the Risk
Access approvals, exception handling, incident triage, and control design stay with qualified engineers who understand both the threat landscape and the standards behind each requirement. The people deciding what a service account may touch or whether an alert is an incident are accountable for the call and can defend it to an assessor.
Evidence That Accumulates
Control activity, access decisions, and configuration changes are logged in real time, automatically building your SOC 2 or ISO evidence set during daily operations. This is Audit-Ready by Default: the environment carries its own proof, so an audit or questionnaire opens against a record that is already complete.
STRATEGY-TO-EXECUTION STACK
Run Secure and Govern Your Entire Environment
Set the direction with Strategy and Advisory, build repeatable controls with Operations and Process Engineering, automate the routine with Technology and AI, and hold coverage as you grow with Managed Services.
You get every layer covered, from daily IT operations to security and identity to governance.
IT Helpdesk and End-User Support
Tiered support that resolves user issues against defined SLAs, with ticket data surfacing recurring problems worth engineering out of the environment for good.
Systems and Endpoint Administration
Servers, workstations, and mobile devices administered to a known baseline, with patching, imaging, and configuration held to a standard across every device in the organization.
Cloud Infrastructure Management
Cloud environments provisioned, monitored, and cost-governed against defined configuration standards so capacity, availability, and spend stay inside approved limits.
Identity and Access Management
Provisioning, deprovisioning, and periodic access reviews run on a fixed cadence, ensuring entitlements match current roles and departed users lose access the day they leave.
Information Security Management
Security controls designed, deployed, and monitored across the environment (from endpoint protection to logging and alerting) aligned to the risks that apply to your business.
Data Handling and Retention Protocols
Classification, retention, and disposal rules are defined and enforced across all systems, ensuring sensitive data is retained only as long as required and remains easily retrievable for regulatory requests.
Compliance Framework Support
Mapping, implementation, and ongoing maintenance of controls for SOC 2, ISO 27001, HIPAA, and similar frameworks, run as continuous operations year-round.
Security Audit and Assessment Support
Preparation and support for external audits, penetration tests, and client security assessments, with evidence organized and remediation tracked to closure.
Technical Resourcing
Skilled engineers and administrators embedded into your operation to run workflows and controls day to day, with process knowledge held in systems your team owns.
WORKS WITH YOUR STACK
Improve Coverage Without Replacing Your Stack
Platform-agnostic. Solutions are designed around the systems already in place. Where a platform change is in scope, the same team can advise on what to move to and why.


Disclaimer: All product names, logos, and brands are property of their respective owners. Use of these names, logos, and brands does not imply endorsement.
CORDATUS DELIVERY METHOD
Disciplined Model for a Resilient IT Infrastructure
Our Method moves an environment from unmapped risk to governed coverage in a set order, closing the highest exposures first and building an evidence trail as it goes.
01
Diagnosis & Value Mapping
Environment gets inventoried end to end, coverage gaps are mapped against applicable frameworks, and risks are ranked by exposure. You receive a clear picture of where endpoints, identities, and evidence stand today alongside the fastest wins.
02
Architecture & Roadmap
Target operating model takes shape so the control set, review cadence, patching schedule, tooling, and evidence trail work together from day one. The roadmap sequences the work so critical risks close first.
03
Integration & Deployment
Workflows go live, tooling connects, all devices and accounts enroll, and controls move into active operation. Automation takes on routine volume while your specialists retain risk decisions.
04
Continuous Optimization
Environment runs on cadence, tuning controls as threats and your infrastructure change. Each assessment opens against a complete record, and coverage holds as you grow.
QUESTIONS
FAQs - Straight Answers on IT and Security
What does Cordatus actually do for our IT and security function?
Cordatus designs and builds the operating system for the function. That covers workflows for provisioning, patching, and support; security controls and monitoring; the review cadence that keeps them honest; and the evidence capture behind it all. Your team retains ownership of risk decisions while routine volume and record-keeping run on defined processes. When additional capacity is needed, the Cordatus managed services group can support day-to-day operations.
Does our IT director stay in control of the environment?
Yes. Your IT director and security lead retains ownership of architecture decisions, risk acceptance, exceptions, and relationships with auditors and clients. The workflows, automation, and controls Cordatus installs carry the volume and hold cadence, allowing the environment to run under your team’s control.
How does Cordatus keep us ready for a SOC 2 or ISO 27001 audit?
Control activity, access reviews, and configuration changes are captured as they happen. When an assessment opens, the evidence set is largely already populated, so the process starts from a complete record and findings lists run shorter. The proof accumulates while the work runs.
What happens to coverage during staff turnover?
Because provisioning, patching, and monitoring follow structured, documented workflows, coverage remains consistent through team transitions. Onboarding a new administrator means learning an established process, ensuring no endpoint or account drops out of scope while a role is vacant.
How fast can Cordatus close the gaps it finds?
The roadmap from the diagnosis phase sequences remediation by risk, ensuring critical exposures close first. You see high-risk items addressed early, with the remaining tail tracked to closure on a schedule your board can follow.
Can Cordatus support us during a client security questionnaire or a pen test?
Yes. Because evidence and control records are kept current, questionnaire responses draw on existing documentation, and penetration tests open against known configurations. Cordatus prepares materials, supports the engagement, and tracks remediation through to closure.
Build an IT Function Where Trust Is Proven, Not Promised
Let’s map where your environment stands now and design an operating model that keeps it covered and provable.